CVE-2023-49276
Attribute Injection leading to XSS(Cross-Site-Scripting)
Impact
### Summary Google Analytics element Attribute Injection leading to XSS ### Details Since the custom status interface can set an independent Google Analytics ID and the template has not been sanitized, there is an attribute injection vulnerability here, which can lead to XSS attacks. 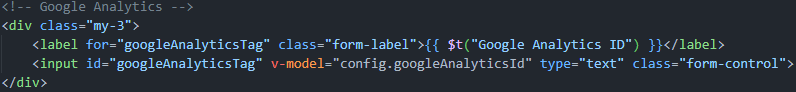 ### PoC 1. Run the latest version of the louislam/uptime-kuma container and initialize the account password. 2. Create a new status page. 3. Edit the status page and change the Google Analytics ID to following payload(it only works for firefox. Any attribute can be injected, but this seems the most intuitive): ``` 123123" onafterscriptexecute=alert(window.name+1),eval(window.name) a="x ``` 4. Click Save and return to the interface. XSS occurs. screenshots:  
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| npm | uptime-kuma | >= 1.20.0, <= 1.23.6 | 1.23.7 |
Affected products
| Vendor | Product | Affected versions |
|---|---|---|
| Uptime.Kuma | Uptime Kuma | from 1.20.0 before 1.23.7 |
Weakness classification
References
- NVD record
- CVE.org record
- GitHub advisory
- https://github.com/louislam/uptime-kuma/commit/f28dccf4e11f041564293e4f407e69ab9ee2277f
- https://github.com/louislam/uptime-kuma/security/advisories/GHSA-v4v2-8h88-65qj
- https://github.com/advisories/GHSA-v4v2-8h88-65qj
- https://nvd.nist.gov/vuln/detail/CVE-2023-49276