CVE-2024-27288
1Panel open source panel project has an unauthorized vulnerability.
Impact
### Impact The steps are as follows: 1. Access https://IP:PORT/ in the browser, which prompts the user to access with a secure entry point. 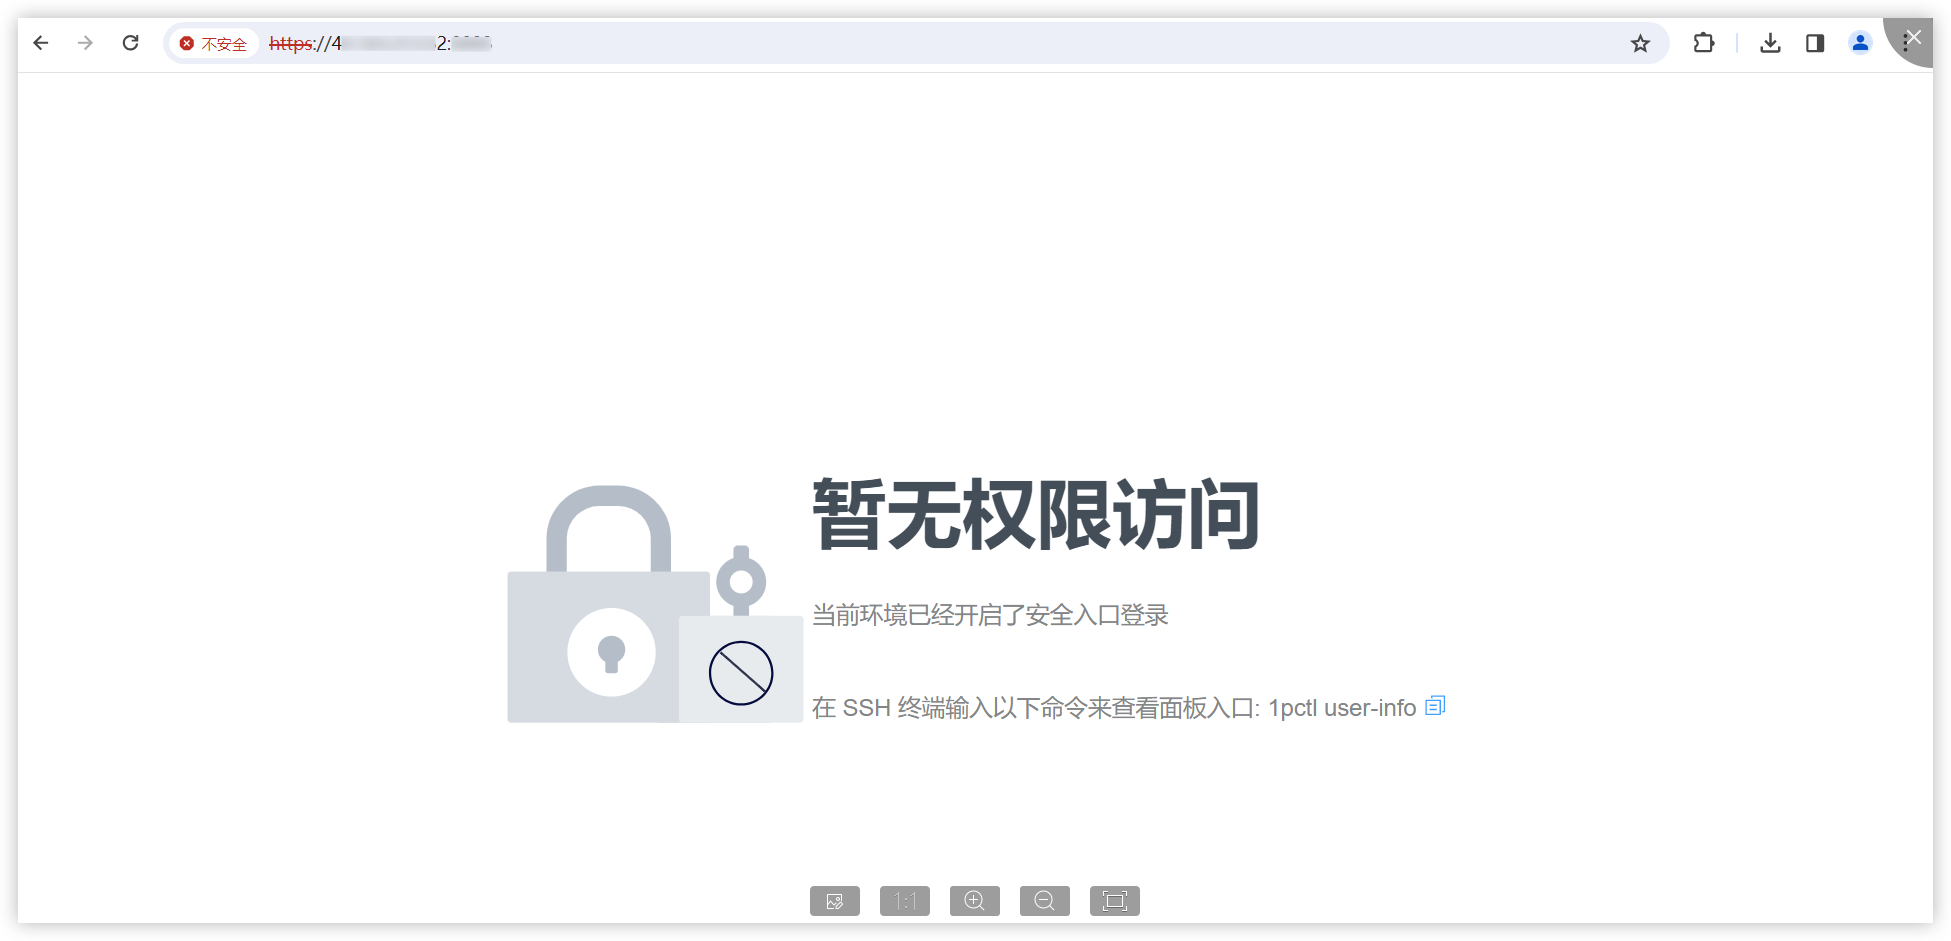 2. Use Burp to intercept: 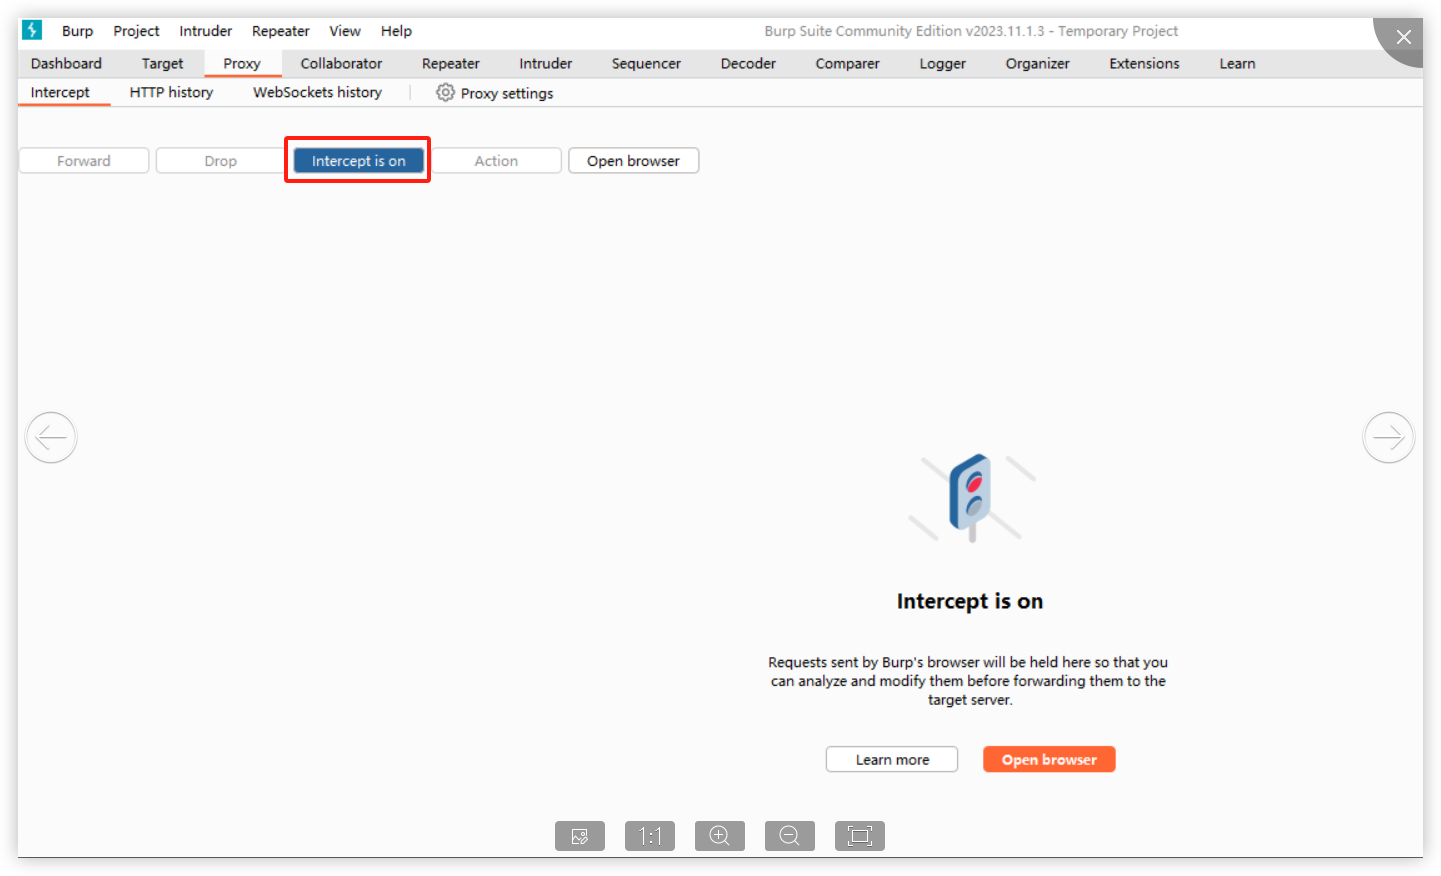 When opening the browser and entering the URL (allowing the first intercepted packet through Burp), the following is displayed: 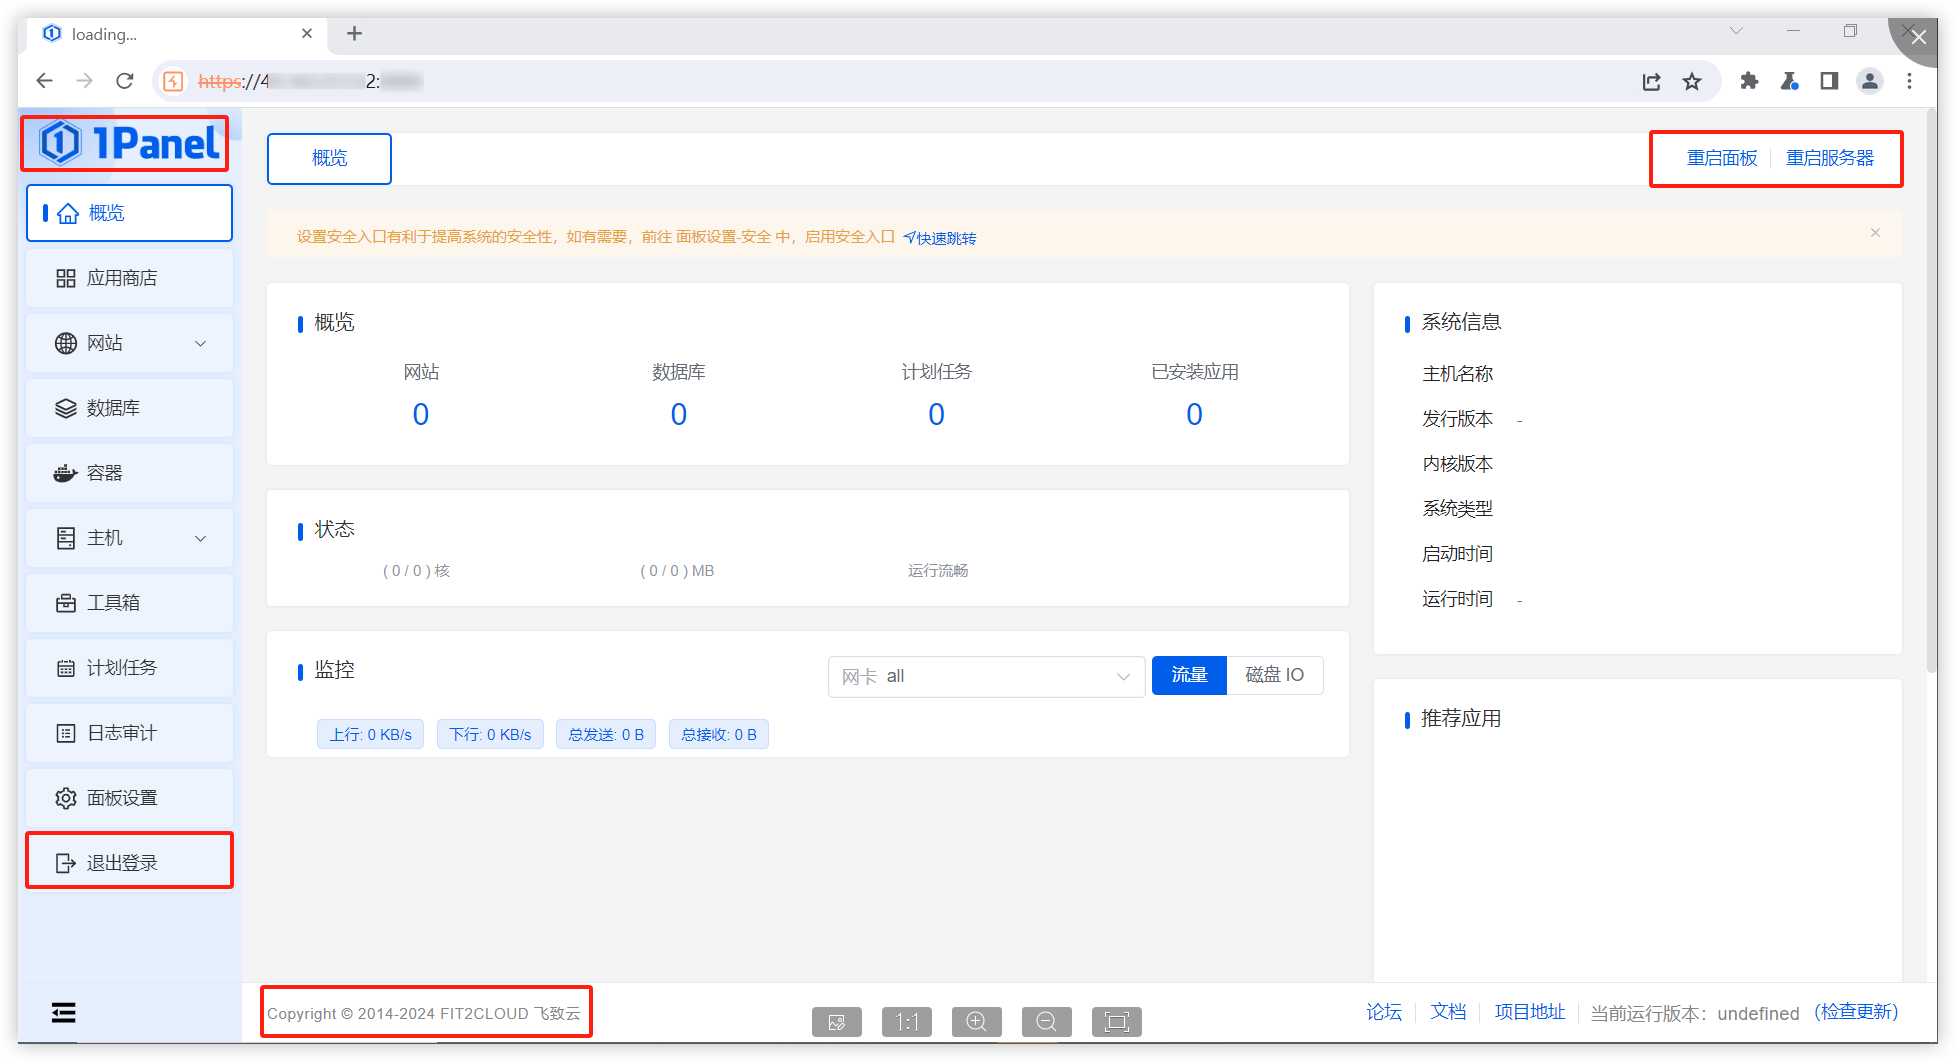 It is found that in this situation, we can access the console page (although no data is returned and no modification operations can be performed)." Affected versions: <= 1.10.0-lts ### Patches The vulnerability has been fixed in v1.10.1-lts. ### Workarounds It is recommended to upgrade the version to 1.10.1-lts. ### References If you have any questions or comments about this advisory: Open an issue in https://github.com/1Panel-dev/1Panel Email us at wanghe@fit2cloud.com
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| go | github.com/1Panel-dev/1Panel | <= 1.10.0-lts | 1.10.1-lts |
Affected products
| Vendor | Product | Affected versions |
|---|---|---|
| Fit2cloud | 1panel | before 1.10.1-lts |
Weakness classification
References
- NVD record
- CVE.org record
- GitHub advisory
- https://github.com/1Panel-dev/1Panel/releases/tag/v1.10.1-lts
- https://github.com/1Panel-dev/1Panel/security/advisories/GHSA-26w3-q4j8-4xjp
- https://github.com/advisories/GHSA-26w3-q4j8-4xjp
- https://nvd.nist.gov/vuln/detail/CVE-2024-27288
- https://github.com/1Panel-dev/1Panel/pull/4014