medium4.3
CVE-2024-28106
phpMyFAQ Stored Cross-site Scripting at FAQ News Content
Impact
### Summary By manipulating the news parameter in a POST request, an attacker can inject malicious JavaScript code. Upon browsing to the compromised news page, the XSS payload triggers. ### PoC 1. Edit a FAQ news, intercept the request and modify the `news` parameter in the POST body with the following payload: `%3cscript%3ealert('xssContent')%3c%2fscript%3e` 2. Browse to the particular news page and the XSS should pop up. 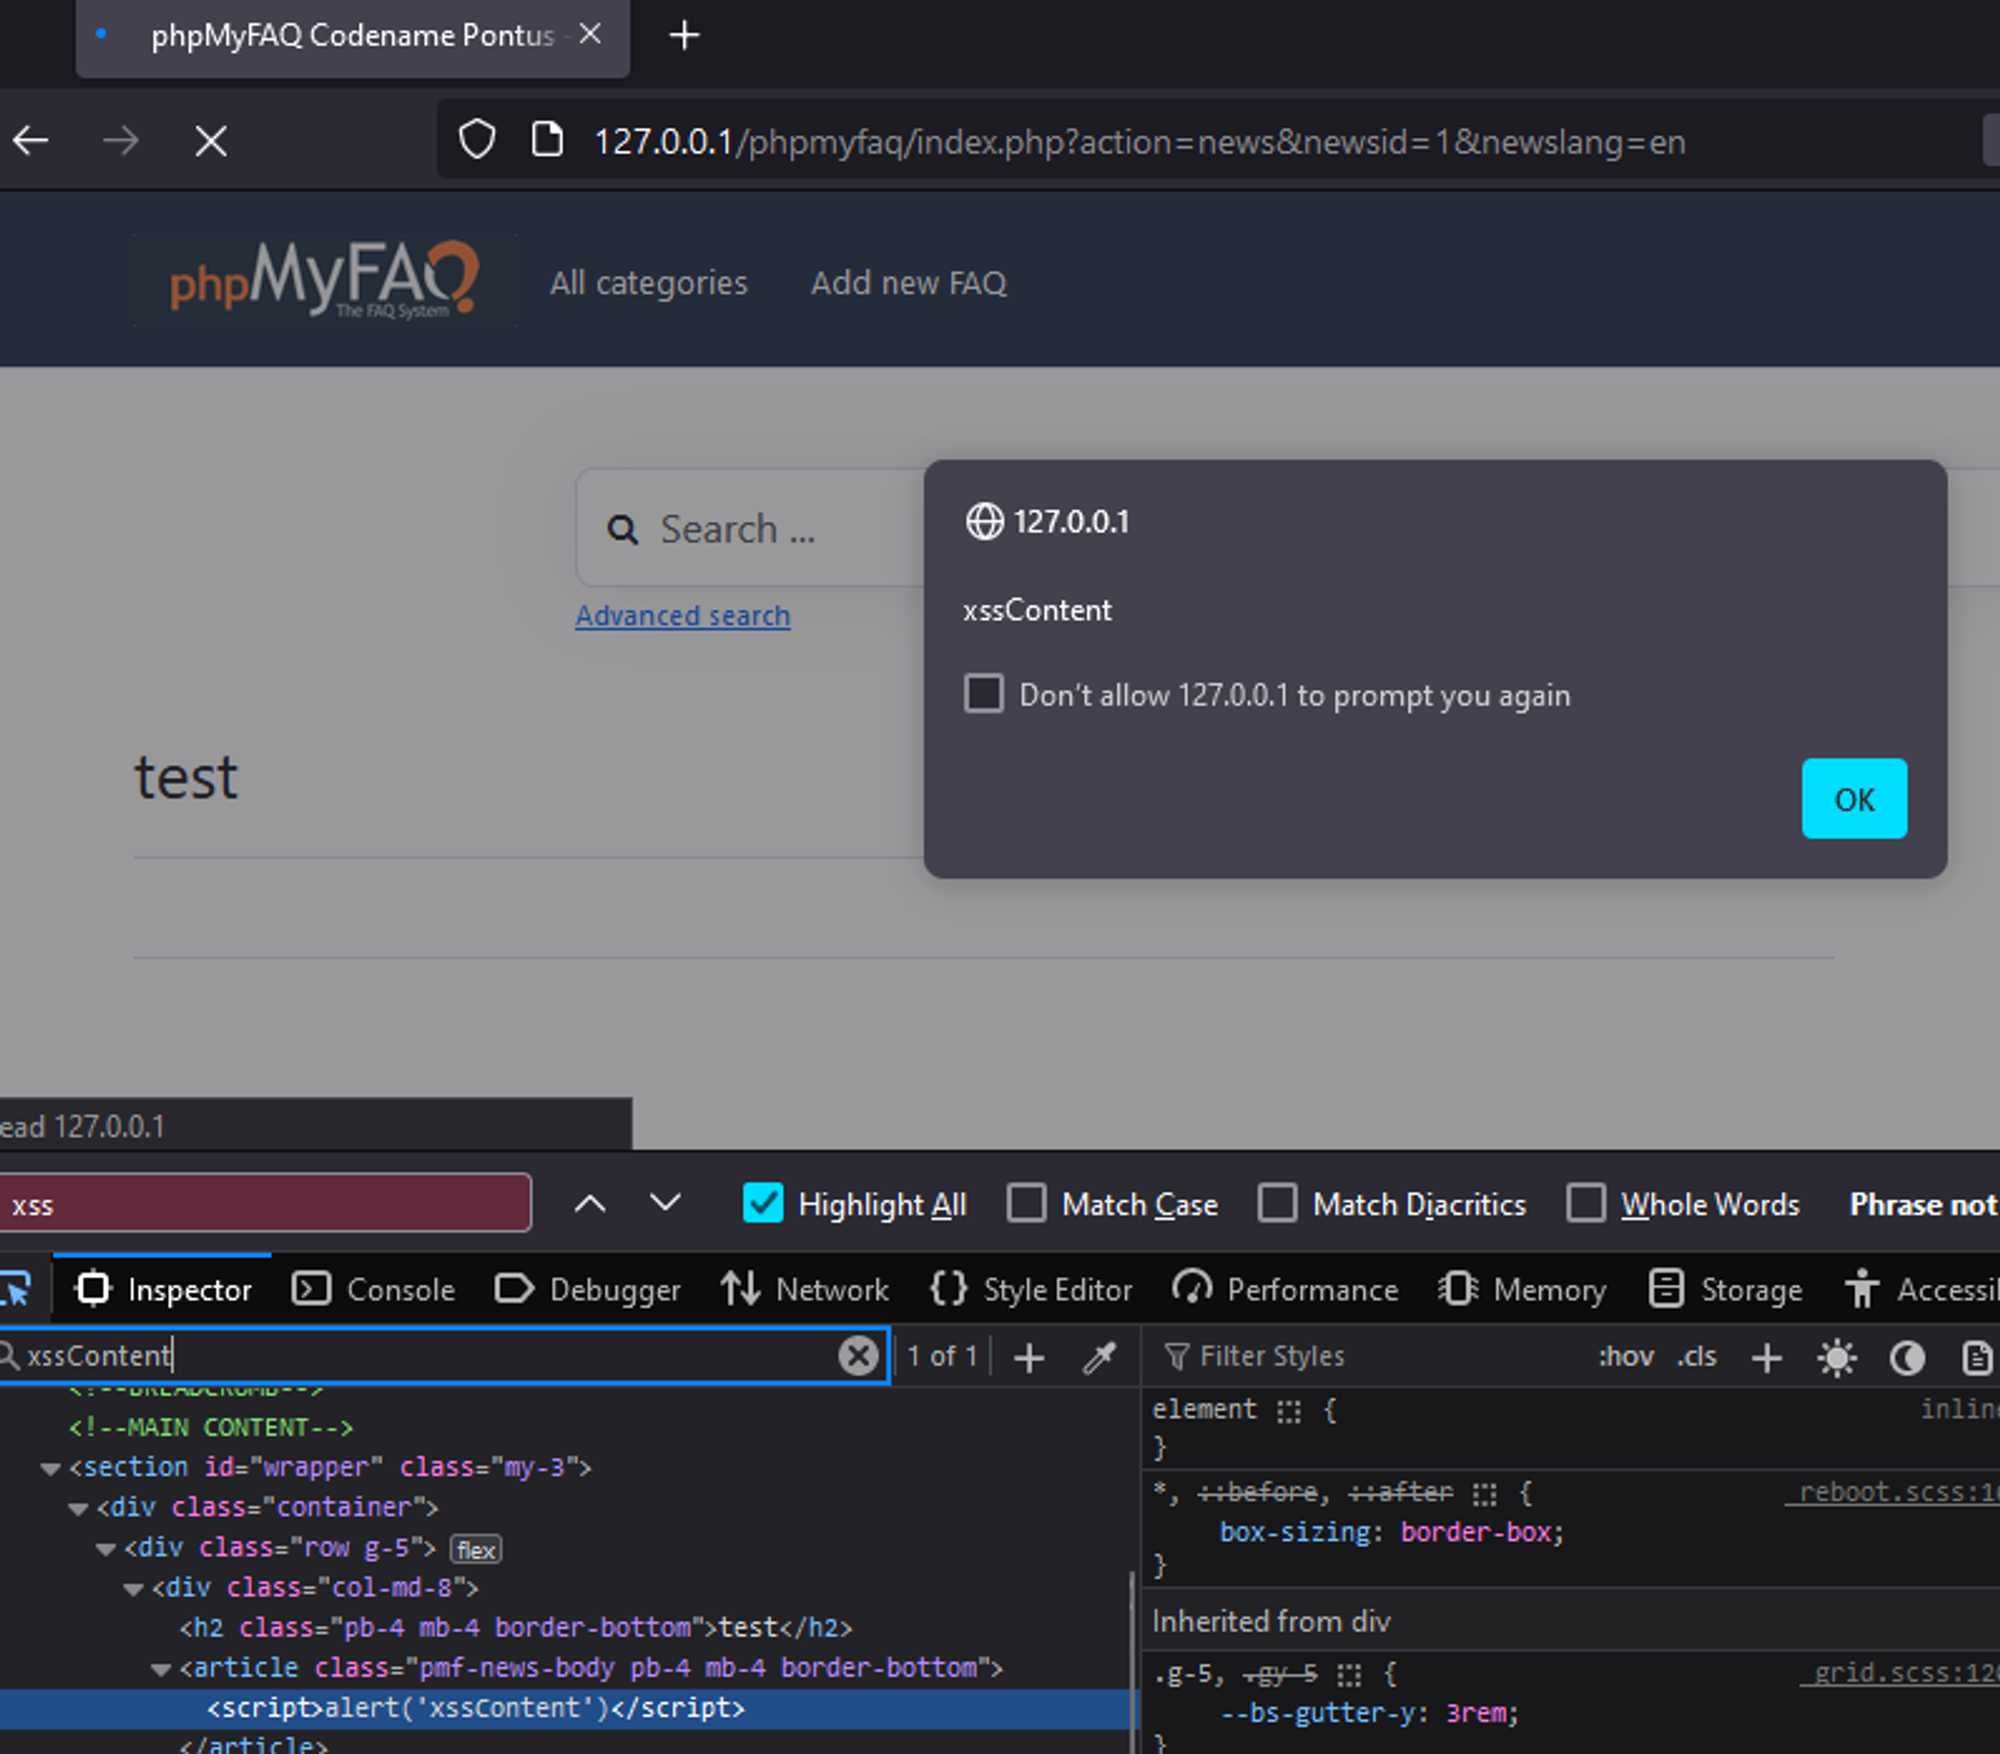 ### Impact This allows an attacker to execute arbitrary client side JavaScript within the context of another user's phpMyFAQ session
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| composer | phpmyfaq/phpmyfaq | = 3.2.5 | 3.2.6 |
Affected products
| Vendor | Product | Affected versions |
|---|---|---|
| Phpmyfaq | Phpmyfaq | Version 3.2.5 |