CVE-2024-28108
phpMyFAQ Stored HTML Injection at contentLink
Impact
### Summary Due to insufficient validation on the `contentLink` parameter, it is possible for unauthenticated users to inject HTML code to the page which might affect other users. _Also, requires that adding new FAQs is allowed for guests and that the admin doesn't check the content of a newly added FAQ._ ### PoC 1. Browse to ../phpmyfaq/index.php?action=add&cat=0 , enter `https://test.com?p=<h1>HTML_INJECTION</h1>` for the contentLink parameter. 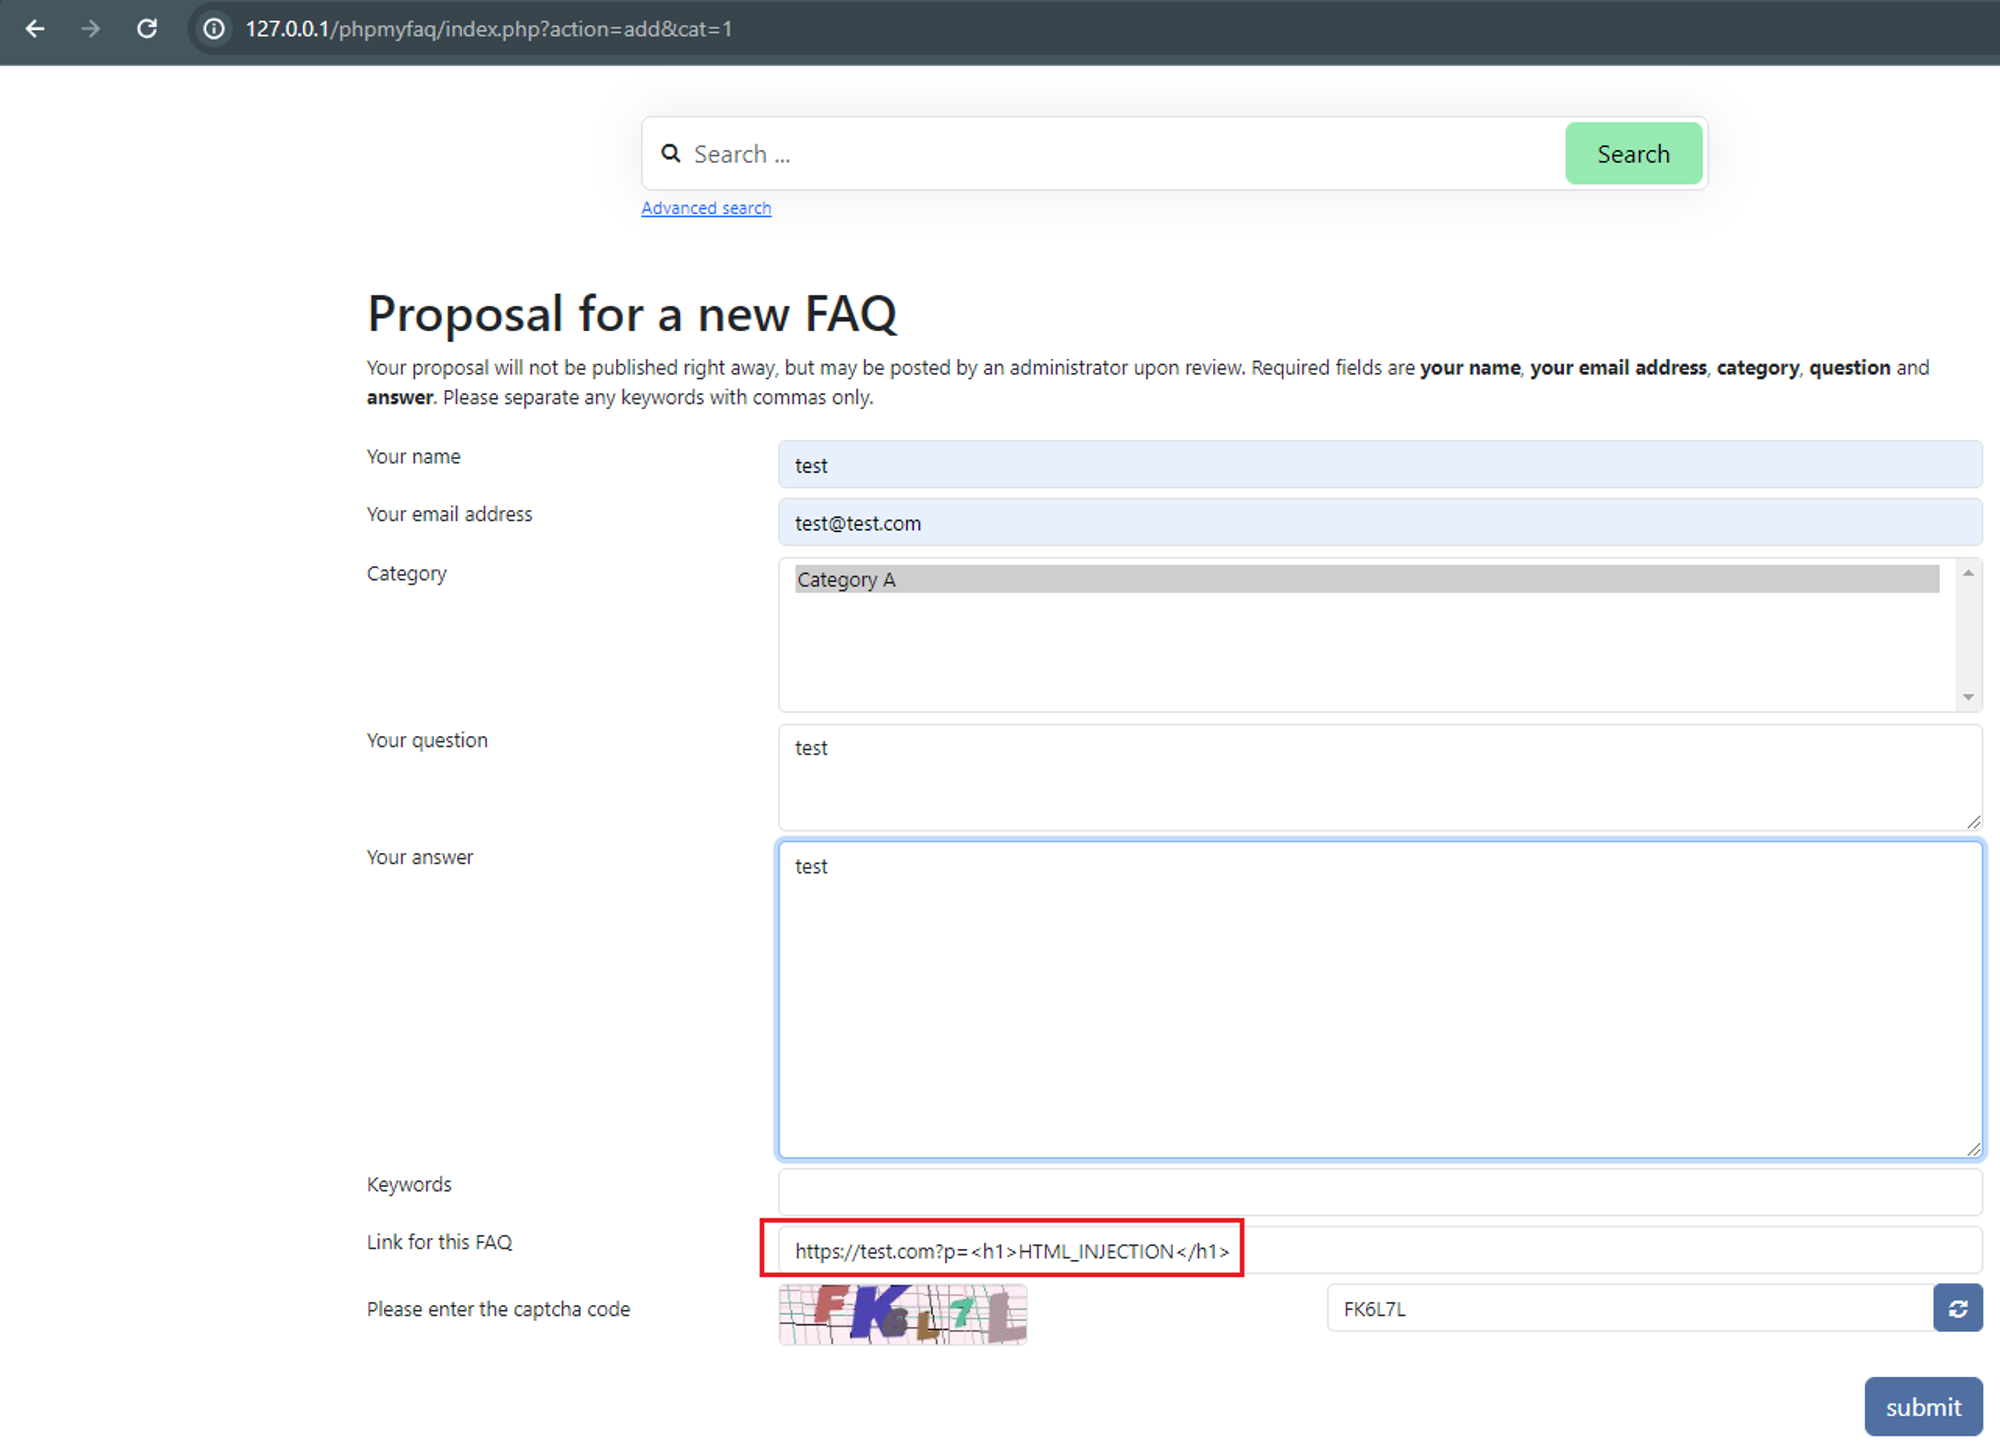 2. Verify the HTML injection by viewing the FAQ itself, “All categories” → “CategoryName” → ”QuestionName”. 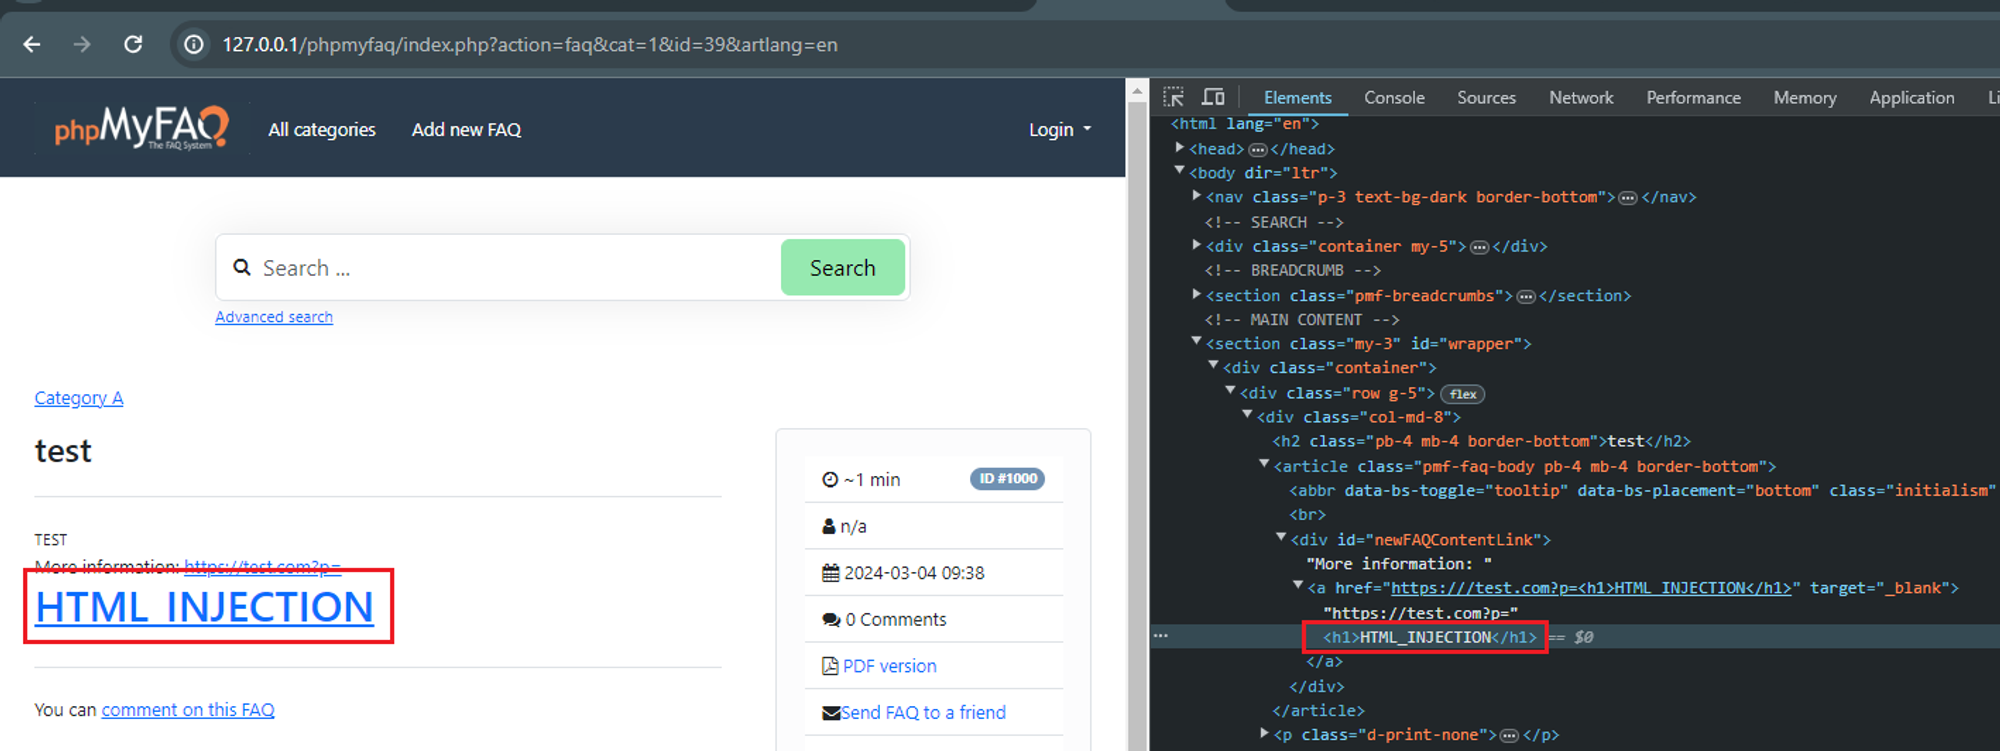 ### Impact Attackers can manipulate the appearance and functionality of web pages by injecting malicious HTML code. This can lead to various undesirable outcomes, such as defacing the website, redirecting users to malicious sites, or altering the content to deceive users. Additionally, unauthenticated HTML injection can compromise user privacy by displaying sensitive information or misleading content. It undermines the integrity of the application and erodes user trust, potentially resulting in loss of reputation and credibility.
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| composer | phpmyfaq/phpmyfaq | = 3.2.5 | 3.2.6 |
Affected products
| Vendor | Product | Affected versions |
|---|---|---|
| Phpmyfaq | Phpmyfaq | Version 3.2.5 |