CVE-2024-32461
LibreNMS vulnerable to SQL injection time-based leads to database extraction
Auswirkung
### Summary SQL injection vulnerability in POST /search/search=packages in LibreNMS 24.3.0 allows a user with global read privileges to execute SQL commands via the package parameter. ### Details There is a lack of hygiene of data coming from the user in line 83 of the file librenms/includes/html/pages/search/packages.inc.php 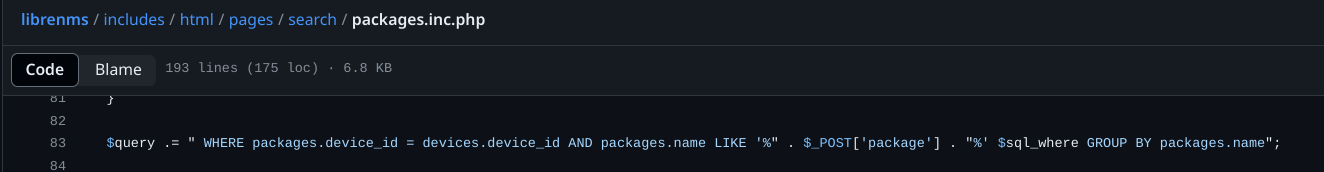 ### PoC https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6 ### Impact With this vulnerability, we can exploit a SQL injection time based vulnerability to extract all data from the database, such as administrator credentials
Ein Angreifer kann die Lücke über das Netzwerk ausnutzen, mit einem normalen Benutzerkonto, ohne Zutun eines Nutzers. Bei Erfolg: hohes Risiko, dass Daten ausgelesen werden, hohes Risiko, dass Daten oder Systeme verändert werden, hohes Risiko für Ausfälle.
Betroffene Pakete
| Ökosystem | Paket | Betroffen | Behoben in |
|---|---|---|---|
| composer | librenms/librenms | < 24.4.0 | 24.4.0 |
Betroffene Produkte · Librenms
| Produkt | Betroffene Versionen |
|---|---|
| Librenms | vor 24.4.0 |
Schwachstellenklasse
Referenzen
- NVD-Eintrag
- CVE.org-Eintrag
- GitHub-Advisory
- https://doc.clickup.com/9013166444/p/h/8ckm0bc-53/16811991bb5fff6
- https://github.com/librenms/librenms/commit/d29201fce134347f891102699fbde7070debee33
- https://github.com/librenms/librenms/security/advisories/GHSA-cwx6-cx7x-4q34
- https://github.com/advisories/GHSA-cwx6-cx7x-4q34
- https://nvd.nist.gov/vuln/detail/CVE-2024-32461