GHSA-fj52-5g4h-gmq8
pyLoad's Session Not Invalidated After Permission Changes
Impact
### Summary The `pyload` application does not properly invalidate or modify sessions upon changes made to a user's permissions. ### Details Whenever an administrator changes the permissions a specific account has, they do not expect that account still being able to access data that their new permissions do not allow. This is not the case for the `pyload` application, as a user with a valid session can still perform the actions. ### PoC Take a user with all the permissions, as shown below. 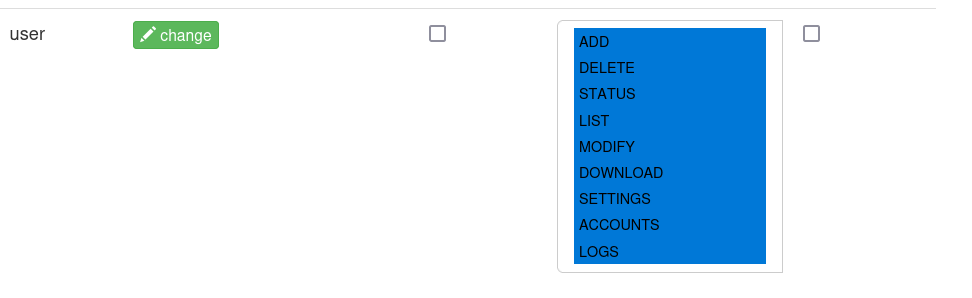 We now log in as this user. 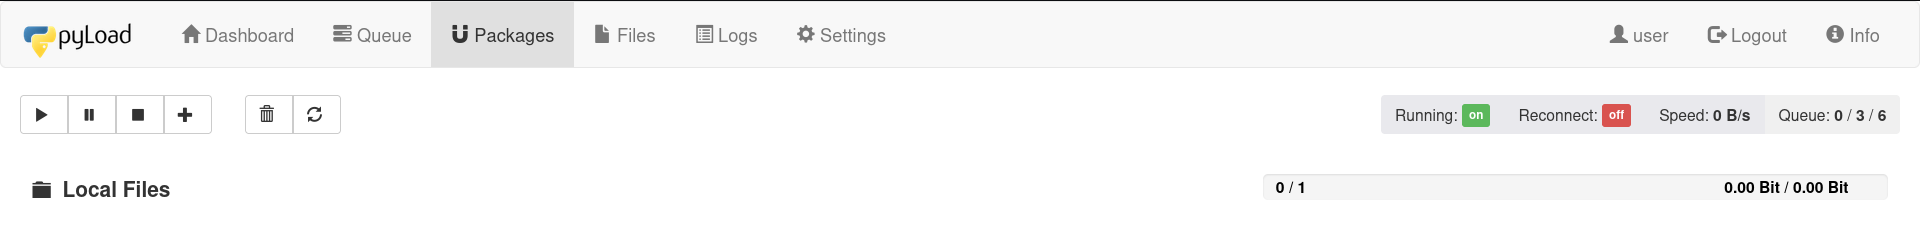 Let us now take away all the permissions. 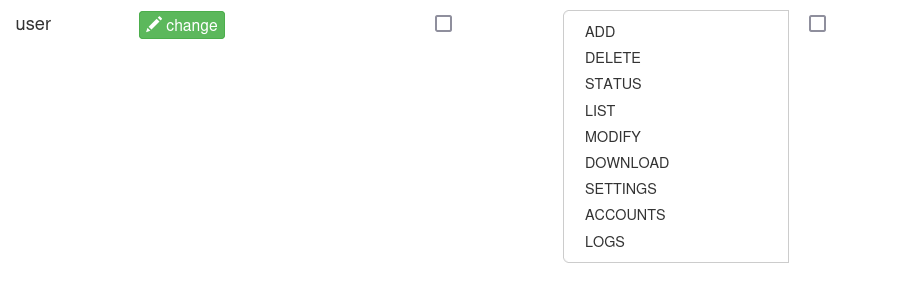 The logged in session can still be used to access everything in the application. 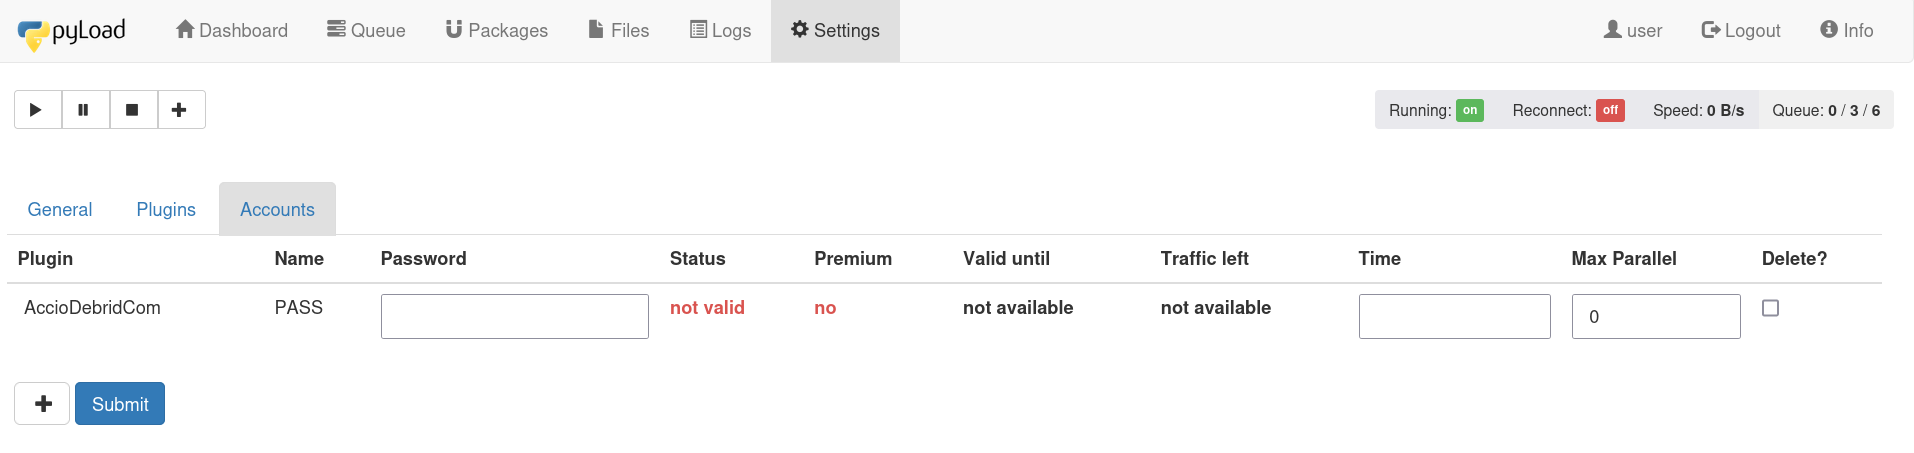 ### Impact Should permissions be taken away, then the user is expected not to be able to execute the actions belonging to those actions anymore.
An attacker can exploit this over the network, without logging in, without any action by a user. Specific conditions have to be met, which makes an attack harder. If it succeeds: low risk of data being read, low risk of data or systems being changed.
Affected packages
| Ecosystem | Package | Affected | Fixed in |
|---|---|---|---|
| pip | pyload-ng | <= 0.5.0b3.dev97 | none recorded |